The problem
Odoo's native security and approval capabilities can become difficult to manage when organizations have complex requirements across users, roles, records, fields, departments, companies, and sensitive business actions. Access policies and approval processes can end up scattered across different configurations and customizations, making them harder to control, audit, and scale.
The solution
Built a unified governance framework that combines access management and approval workflows in one system. Administrators can define what users are allowed to access, assign scoped roles and permissions, and require structured approvals for sensitive actions, changes, or access requests.
What was delivered
✓
Permission & capability management for any Odoo model
✓
Role-based access control with reusable roles
✓
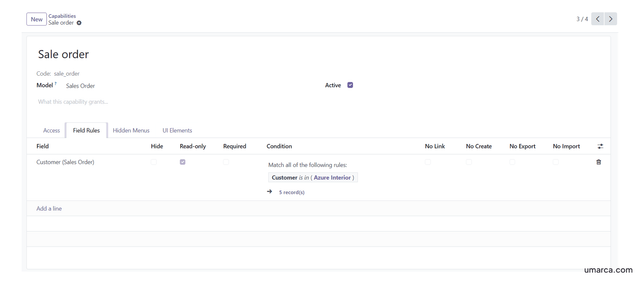
Record-level scopes and restrictions
✓
Field-level visibility, editability, and data-redaction rules
✓
Interface controls for buttons, tabs, menus, views, and search features
✓
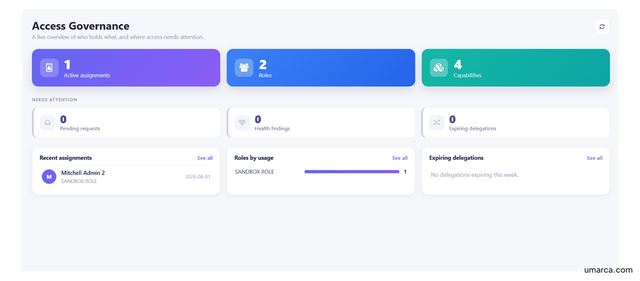
User access assignments with companies, scopes, dates, and delegation
✓
Access request workflows for self-service permission requests
✓
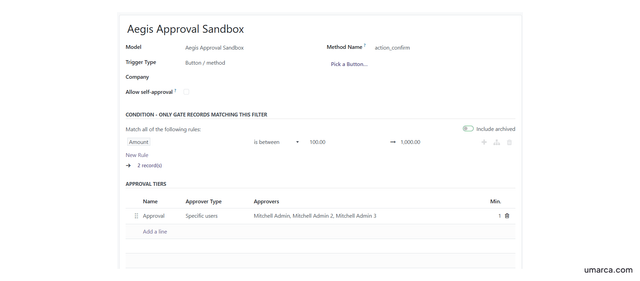
Configurable approval workflows for business actions and sensitive changes
✓
Multi-tier approvals with approver groups, users, managers, and departments
✓
Amount-based approval bands and minimum approver requirements
✓
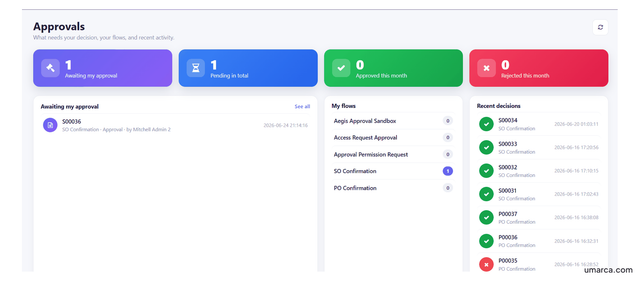
Approver dashboard and worklist
✓
Approval reminders, escalation, and substitute coverage
✓
Email-based approve/reject actions
✓
Login security and governance controls
✓
Health checks and auditing
✓
Native compilation into Odoo's existing security framework
The result
Centralized governance: Access and approval policies managed from one layer
Greater control: Organizations can define what users can access and perform
Structured approvals: Sensitive actions and access requests follow defined approval paths
Improved visibility: Administrators and approvers have clearer oversight of access and pending decisions
Better auditability: Security assignments and approval activity are easier to track
Scalable security model: Reusable roles, capabilities, and scopes simplify management as the organization grows
Reduced configuration fragmentation: Complex security requirements are managed through a consistent framework on top of Odoo’s native security system
Access policies and approval processes were brought into one centralized governance layer, providing greater visibility and consistency over who can access information, perform sensitive actions, and approve them. The framework also creates a more structured foundation for auditing and managing security as the Odoo environment grows.
Available on Odoo Store
Click to visit Odoo App Store Listing